The 4th question requires a 3 digit answer. My nano alert and Snort command lines are correct but I get the number 5. Last night the number was 0.
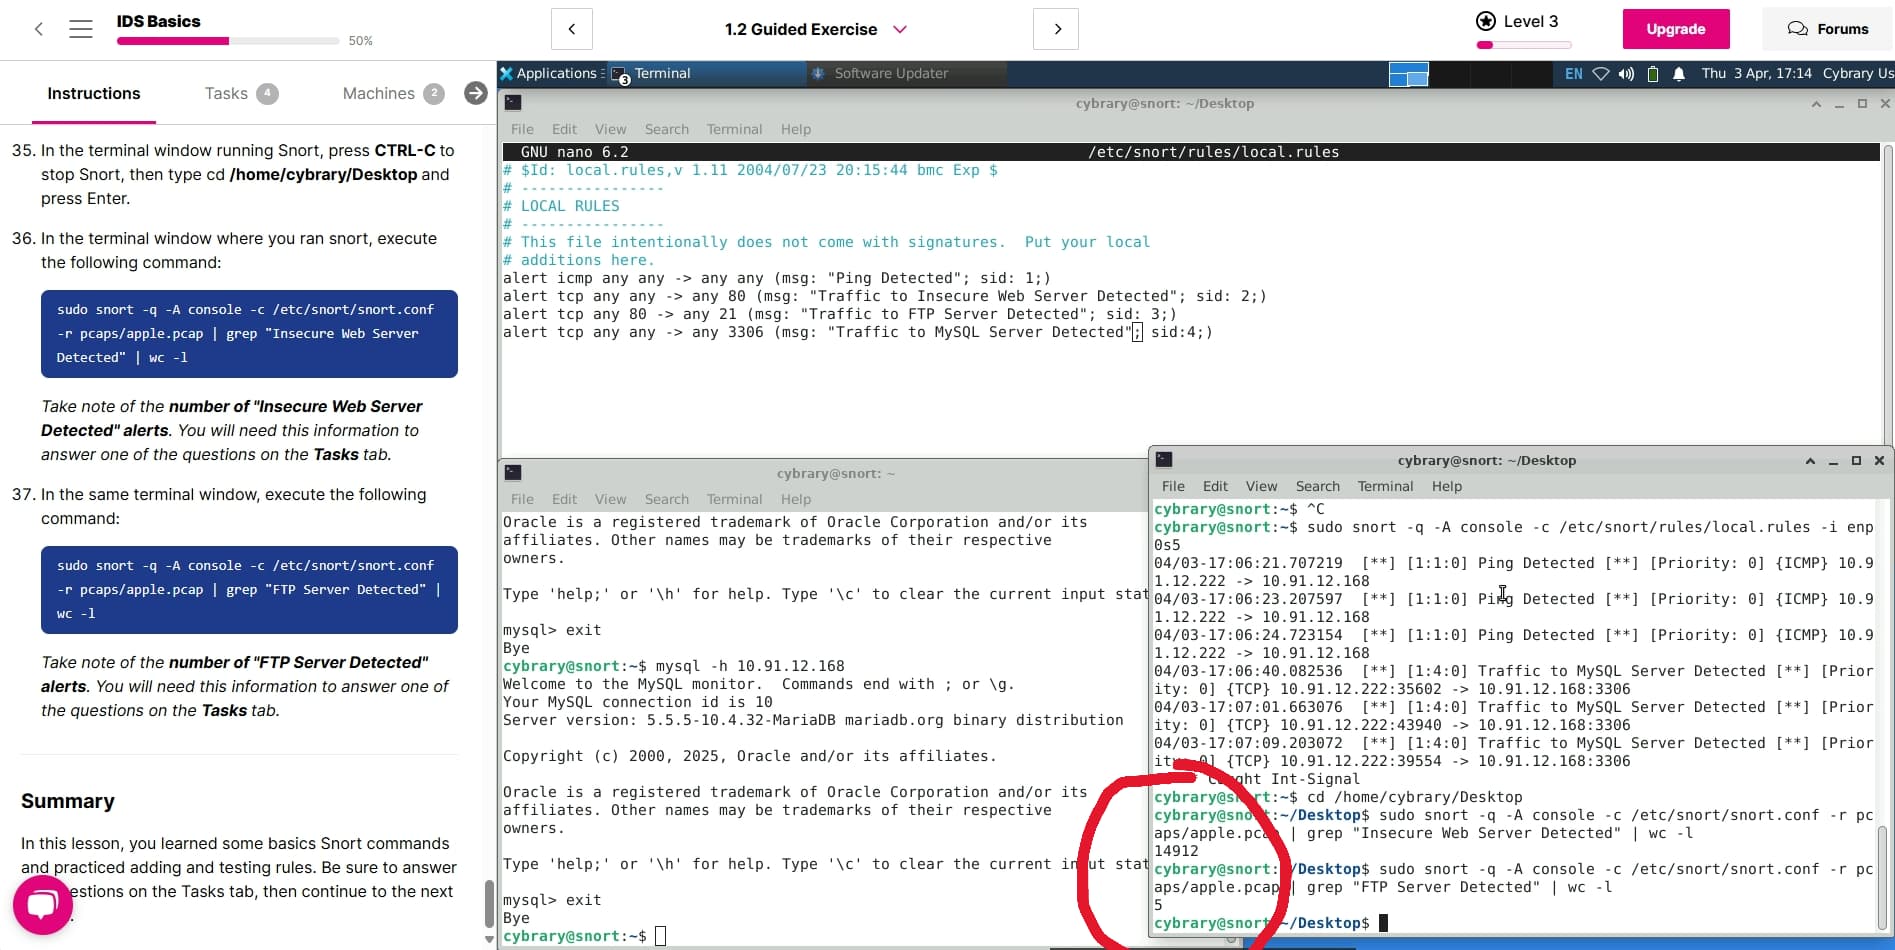
Your FTP rule is wrong:

You have alert tcp any 80 - > any 21
Should be alert tcp any any - > any 21
I think the alert tcp any 80 - > is from earlier in the lab when there were two web traffic rules.
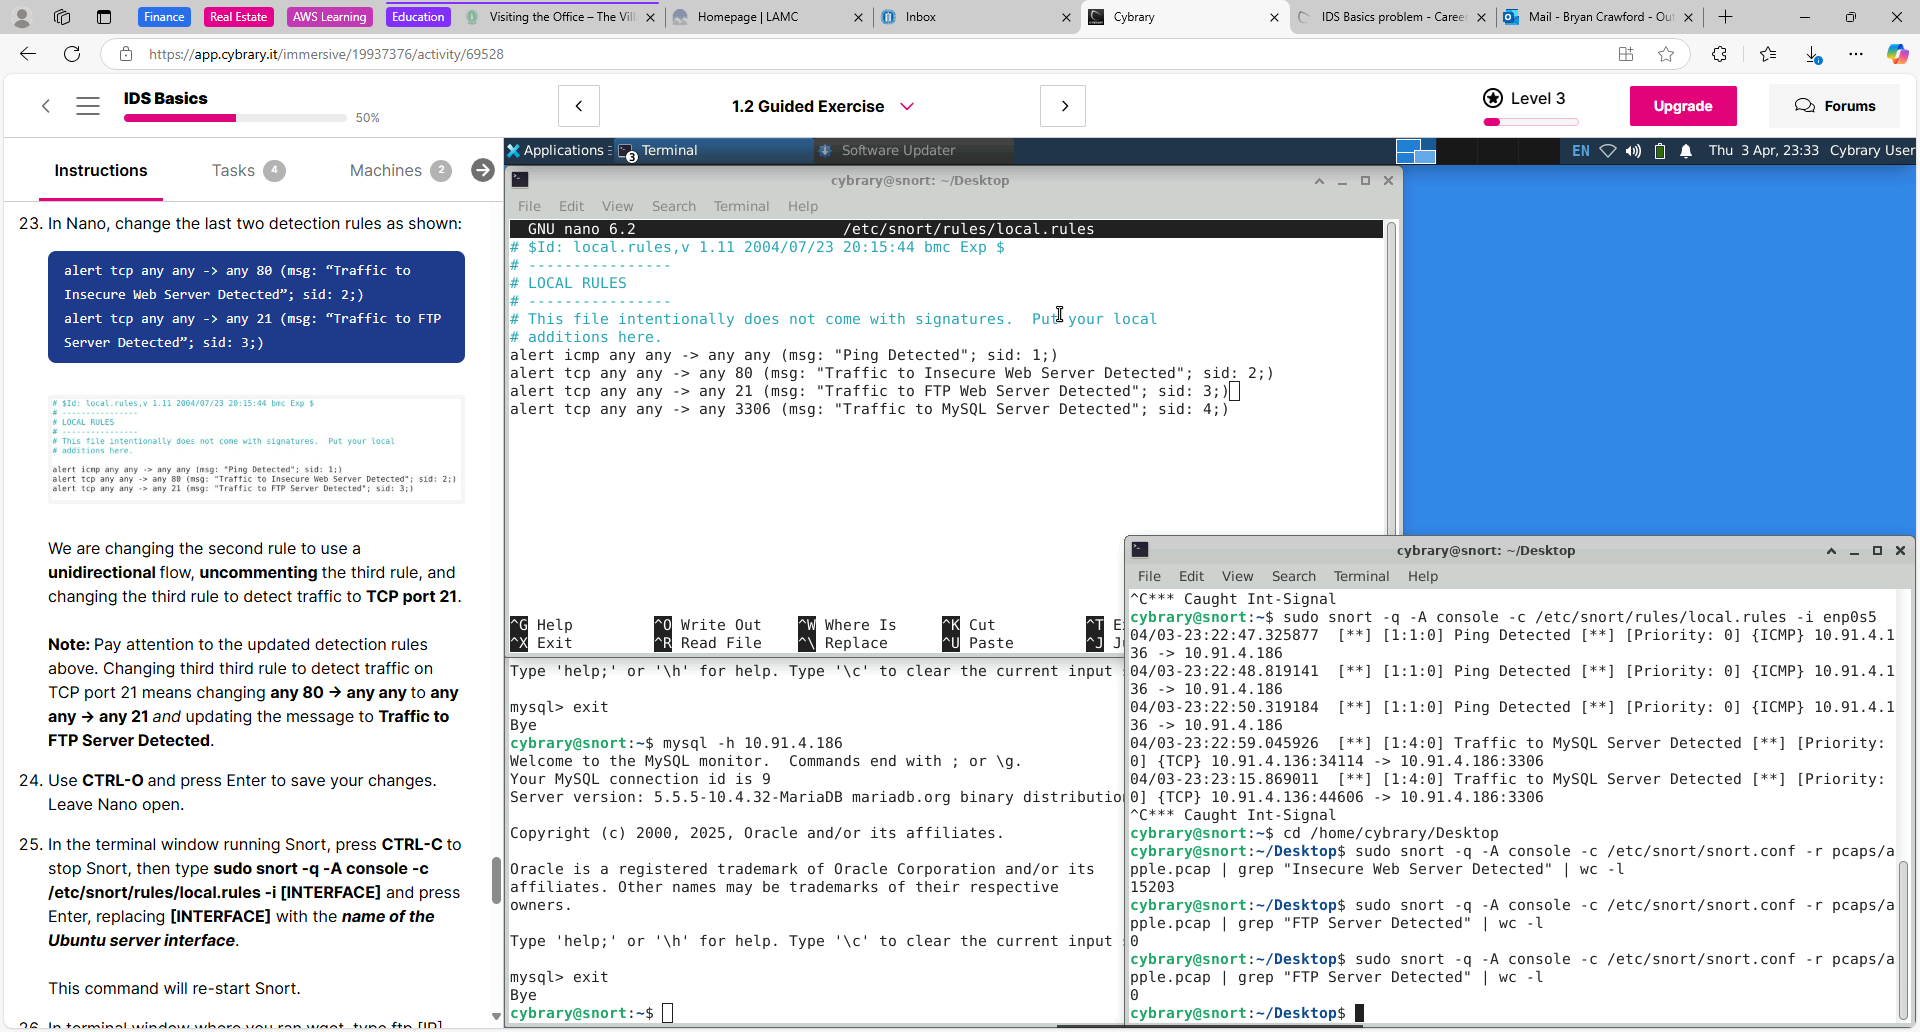
Never mind, I found my last mistake. Thank you for the help!
what was the mistake?? I’m facing the same problem
Incorrect rule description - “Traffic to FTP Web Server Detected” instead of “Traffic to FTP Server Detected”
I’ll message it to you. If you’re getting disconnected frequently, I would recommend trying a different network connection as an initial troubleshooting measure.
Just posting here. I ran into the same problem, and confirm it would definitely be a typo issue in your rule. I realized my rule was set to “any 21 → any any” instead of “any any → any any”. So ensure you’re going to verify that.